I’ve seen many community members talking about this, so first of all, I’m sorry. Yesterday, I was mainly busy posting updates in the group chat and on the official account, and didn’t have time to check the community.
First, here’s an update on the progress:
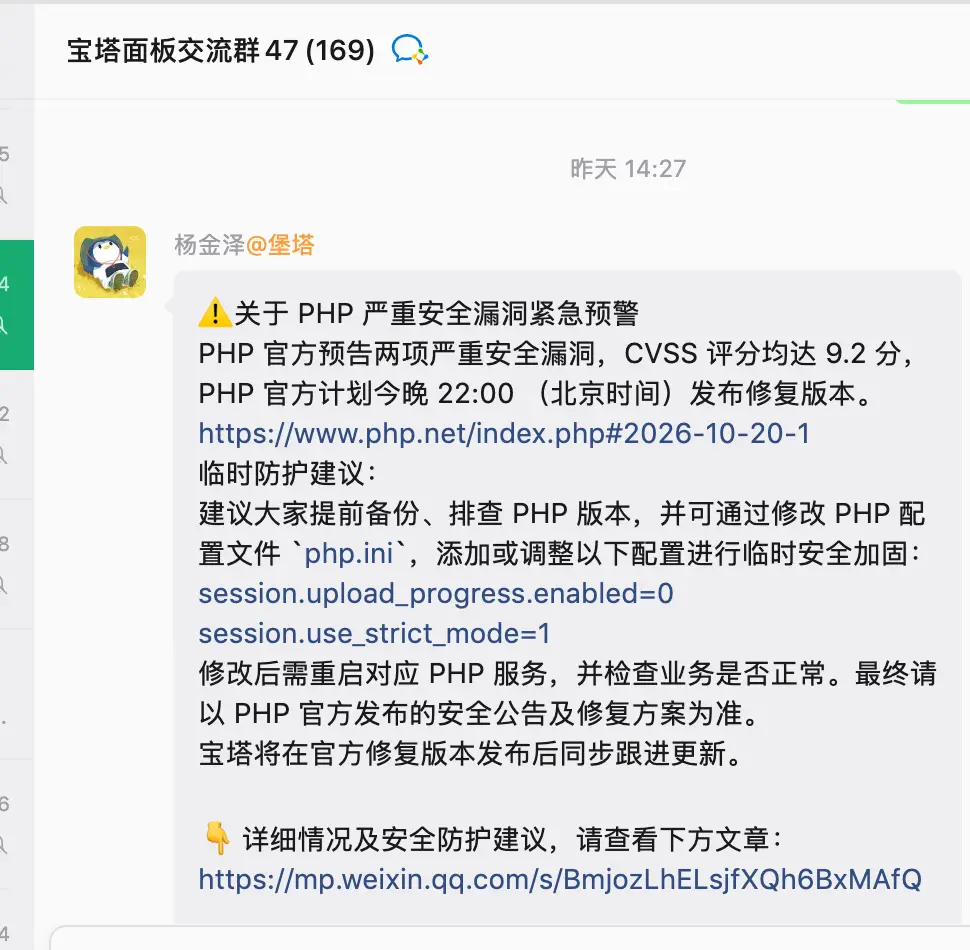
At around 14:47 yesterday, we posted the temporary mitigation plan and announcement in the community group and on the official account.
At around 21:40 last night, monitoring showed that PHP officially released a fix. We then began compilation testing. Since Baota needs to support a large number of systems across many versions, the testing took a little longer than usual.
At around 23:05 last night, we released the fix for version 8.2.
At around 23:20 last night, we released updates for all four versions that are still maintained: 8.2, 8.3, 8.4, and 8.5.
At 23:45, we posted another reminder to upgrade on the official account.
Since the official team only provided patches for versions 7.4, 8.0, and 8.1, we had to package and test those patches ourselves, which took a little longer.
At around 01:38, we released the fixes for the three versions mentioned above.
We’d like to remind everyone to upgrade as soon as possible and not take any chances. Yesterday, we discovered suspected cases of intrusion and exploitation in the community. We also recommend migrating to versions that are still actively maintained.
With the rapid development of AI technology, the speed at which security vulnerabilities are discovered and exploited continues to increase. We strongly recommend that users migrate their services to versions still within the official security maintenance period as soon as possible, to avoid facing greater security risks because older versions are no longer maintained and cannot receive security patches in time.